DarkwyreUAM.
One console for visibility, detection and posture — live across every endpoint, triaged by risk, and self-hosted, so your data stays yours.
Self-hosted · Multi-tenant · Active Directory · Audit-ready. Built for departments that triage by risk, not by chronology.
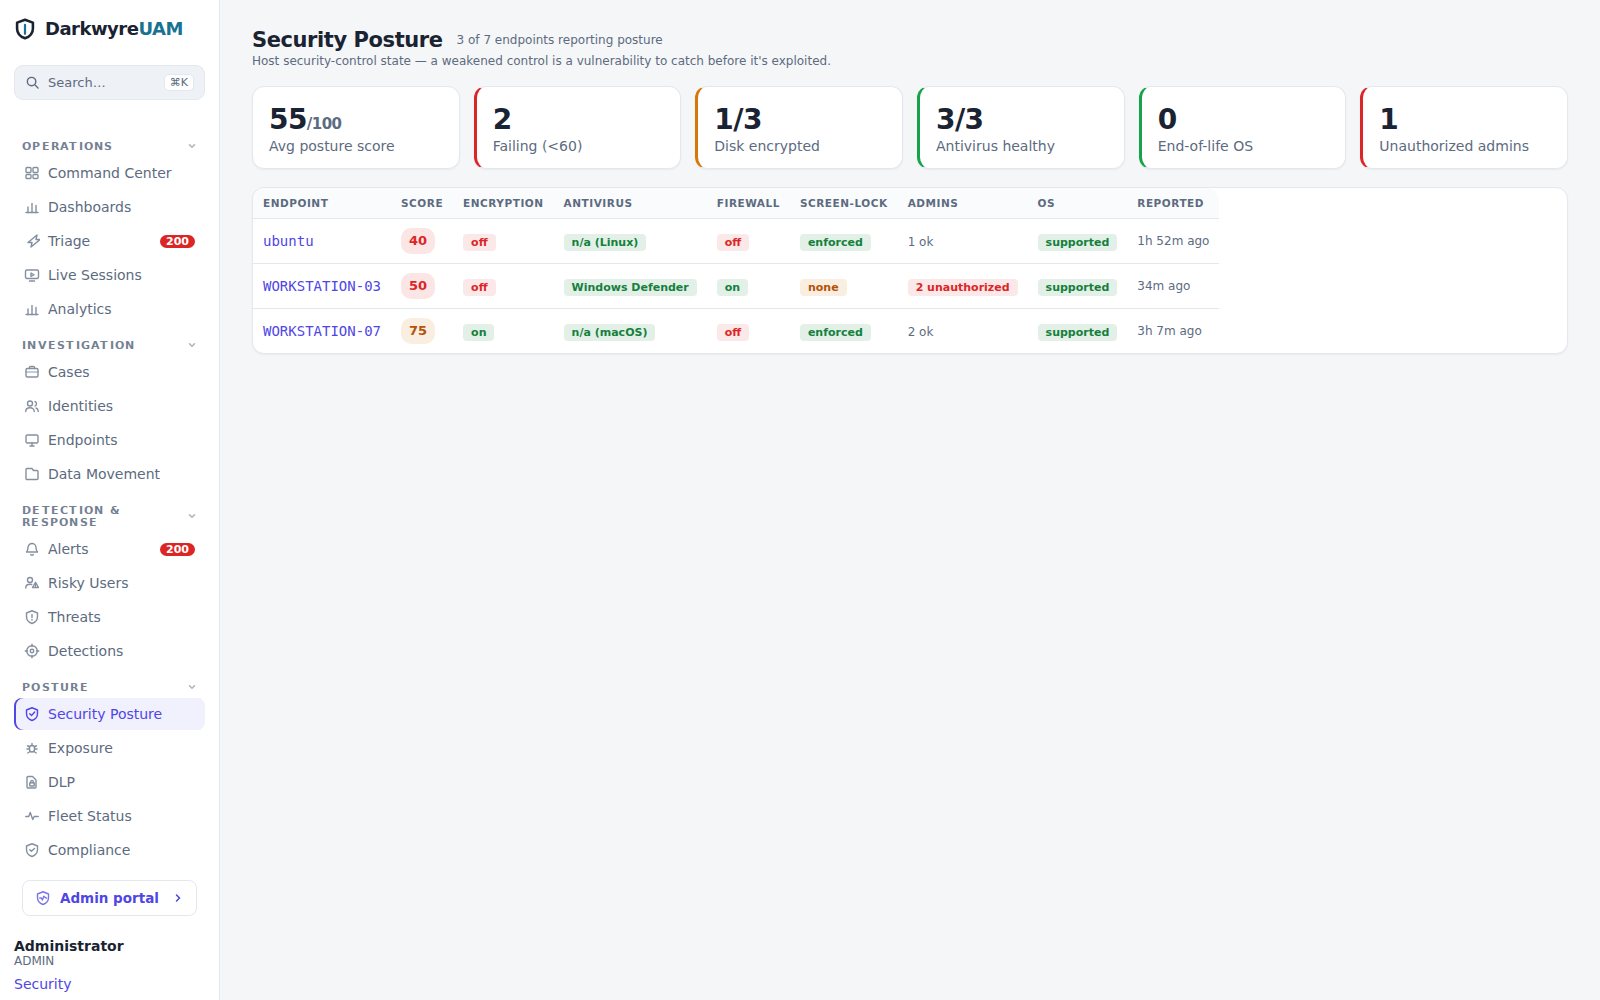 Security posture — control state per endpoint
Live fleet visibility
Every endpoint reporting and clock-synced, with per-device drill-down into processes, network, accounts and app events.
Threat detection that acts early
Authentication and privileged-activity signals surface as alerts by severity, with active credential-attack indicators and attacking-source rollups.
Security-posture scoring
An average posture score across the fleet from antivirus health, firmware, autologon, clock skew and other configuration signals.
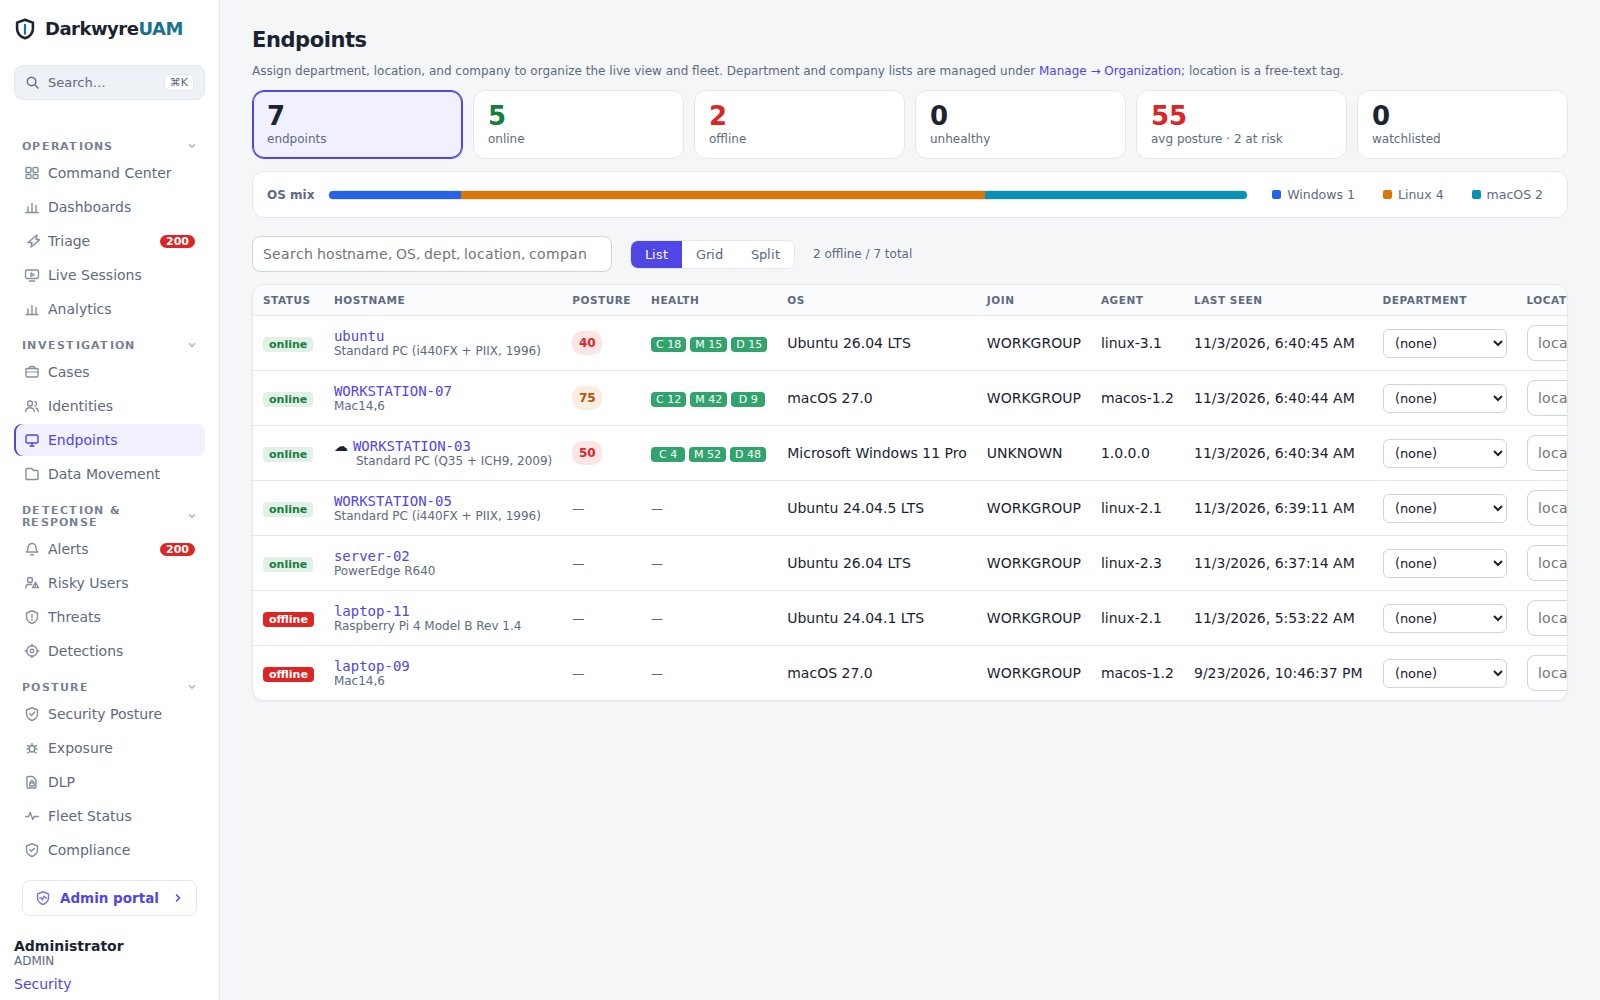 Fleet overview — endpoints, posture and status
Data-loss controls
Policy-driven controls to block USB and removable writes, block cloud and file-transfer uploads, and block printing — per department.
Canary tripwires
Conditions that flag captured activity the moment a rule fires, with a coach message shown to the user when appropriate.
Remote support
Assist a user or take mouse-and-keyboard control of a session when authorized — every action is logged.
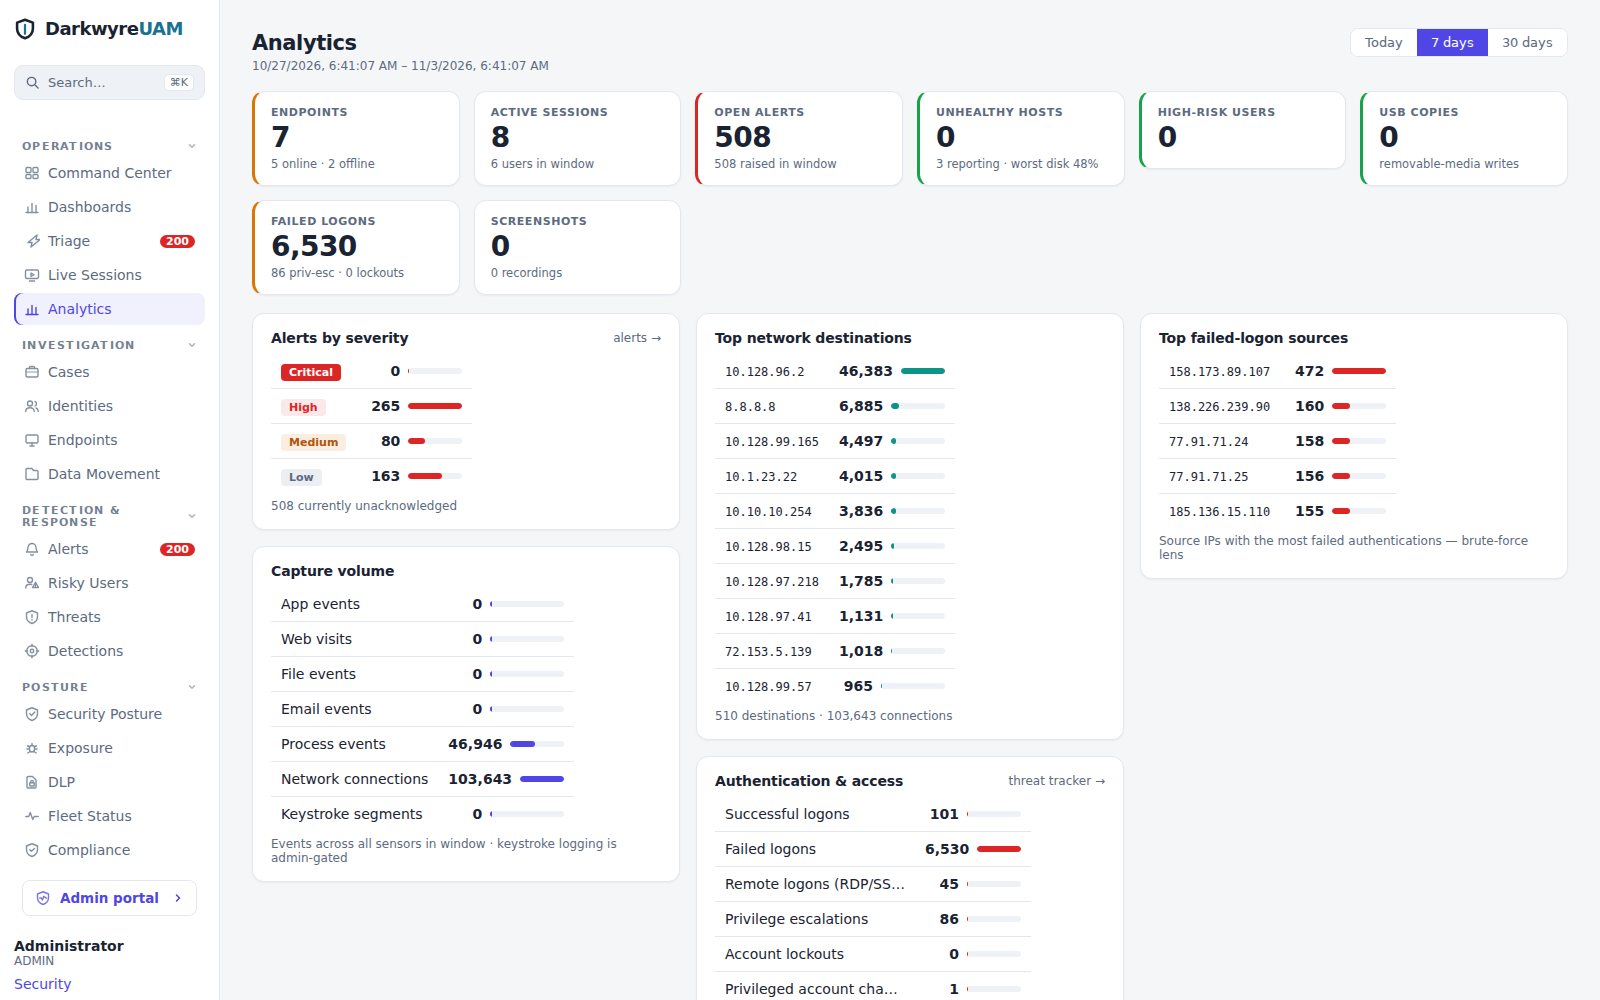 Analytics — risk and activity trends
Multi-tenant & Active Directory
Run single- or multi-tenant, organize endpoints by department, and map identity to AD domain and SID.
Audit, retention & roles
An audit-ready trail with integrity checks, a retention policy per data class, and separate Administrator and Auditor roles that keep operations and oversight distinct.
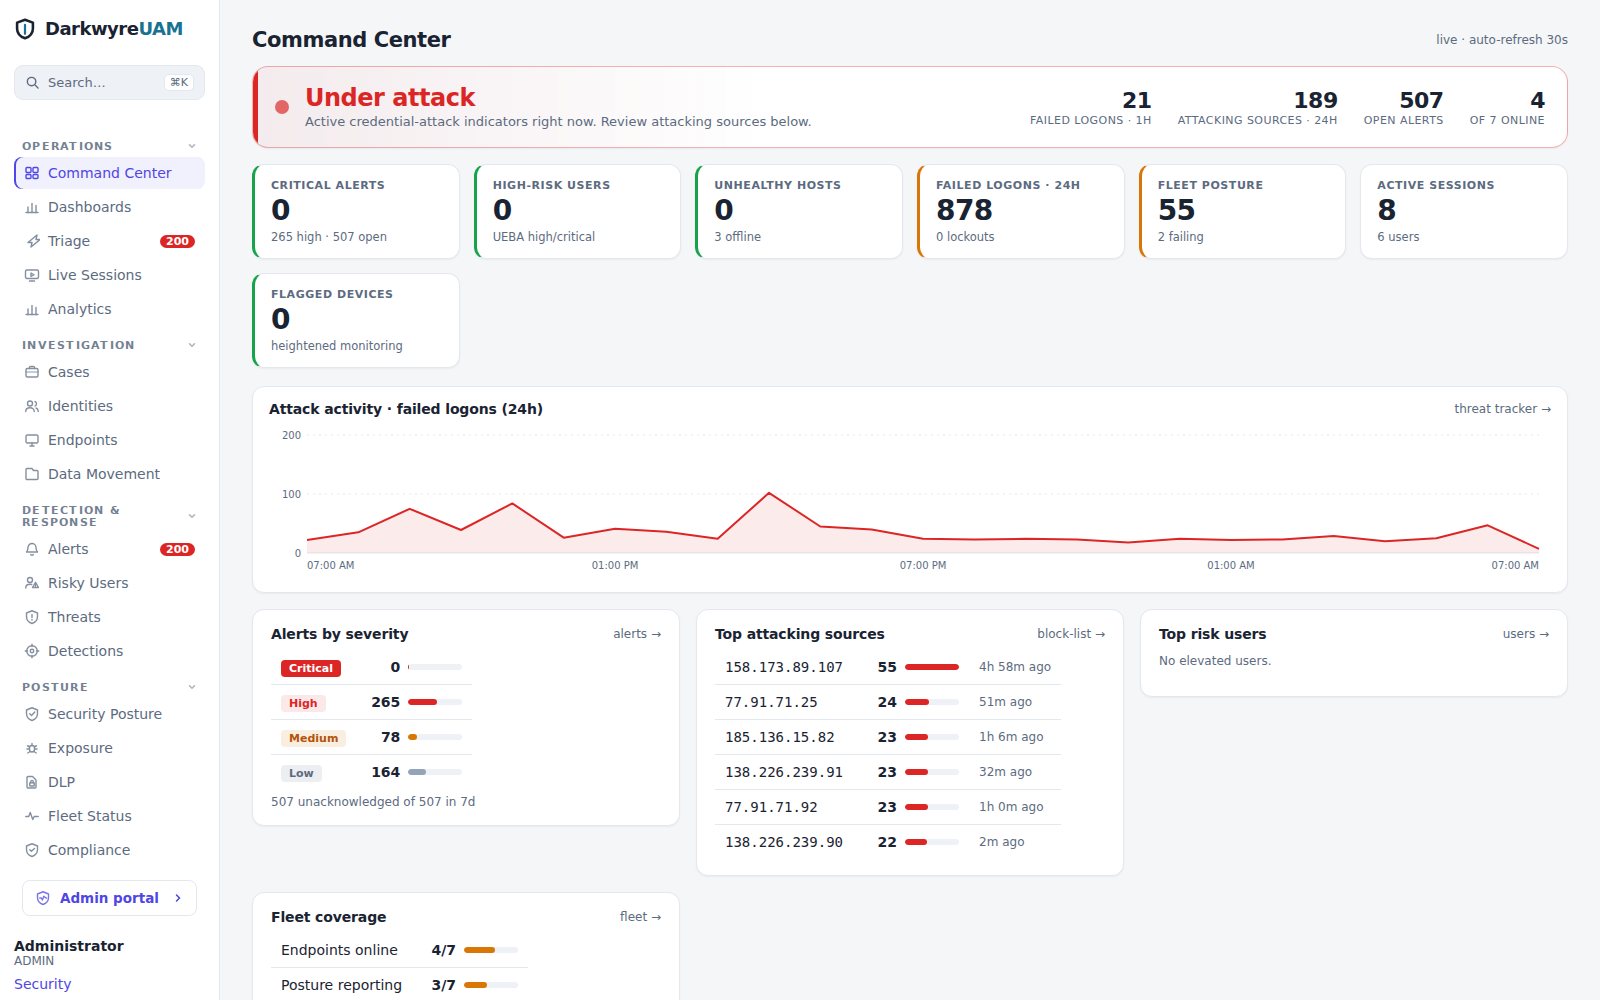 Command Center — the live attack picture
Monitoring your people can trust.
Sign in to your UAM console at uam.darkwyre.com.
 DARKWYRE